


With cybercrime on the rise, breaches of mission‑critical systems can threaten public safety. In light of the government’s The Protection of Critical Infrastructures (Computer Systems) Ordinance announced earlier this year, industry experts are calling on organisations to build more resilient data infrastructure to meet the rules and to prepare for future threats.
Key industry perspectives
Elevating best practice to law: Valerie Yuen, General Manager for Hitachi Vantara Hong Kong & Macau, notes the regulation essentially formalises long‑standing security practices into statutory requirements to strengthen the overall protection framework. While detailed implementation guidance is still being finalised by authorities, organisations should start preparing now.
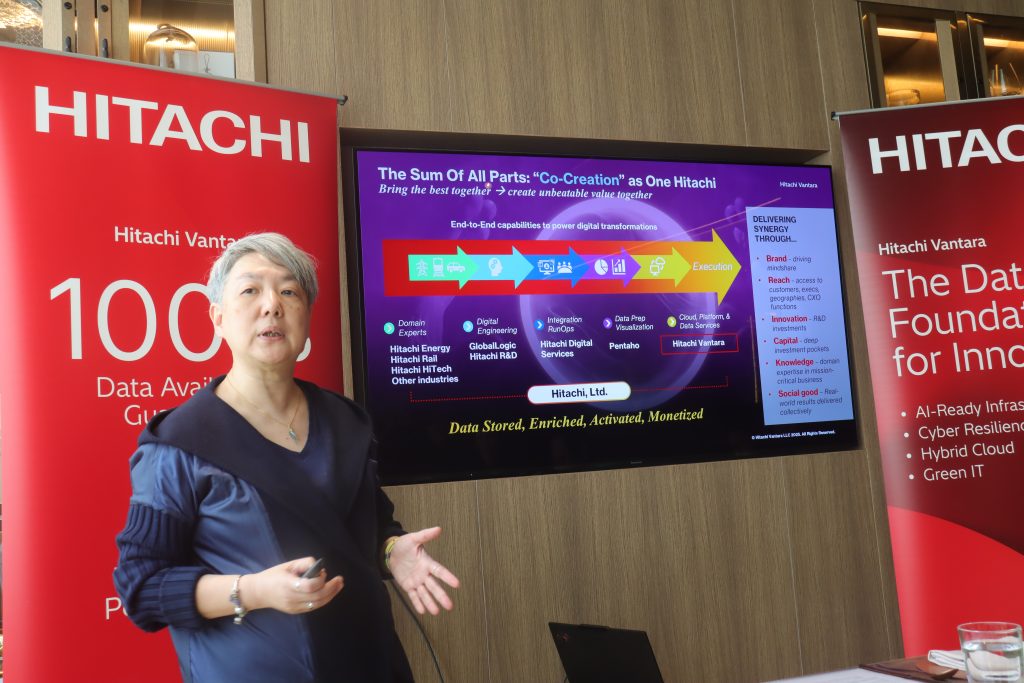
Major risk categories: Valerie highlights two primary risk vectors in today’s market — supply‑chain vulnerabilities and AI‑related threats — the latter of which is becoming increasingly severe. She urges operators of critical infrastructure and large enterprises to proactively build resilient data platforms that comply with the upcoming regulatory requirements and can withstand emerging cyber threats.
Operational recommendations
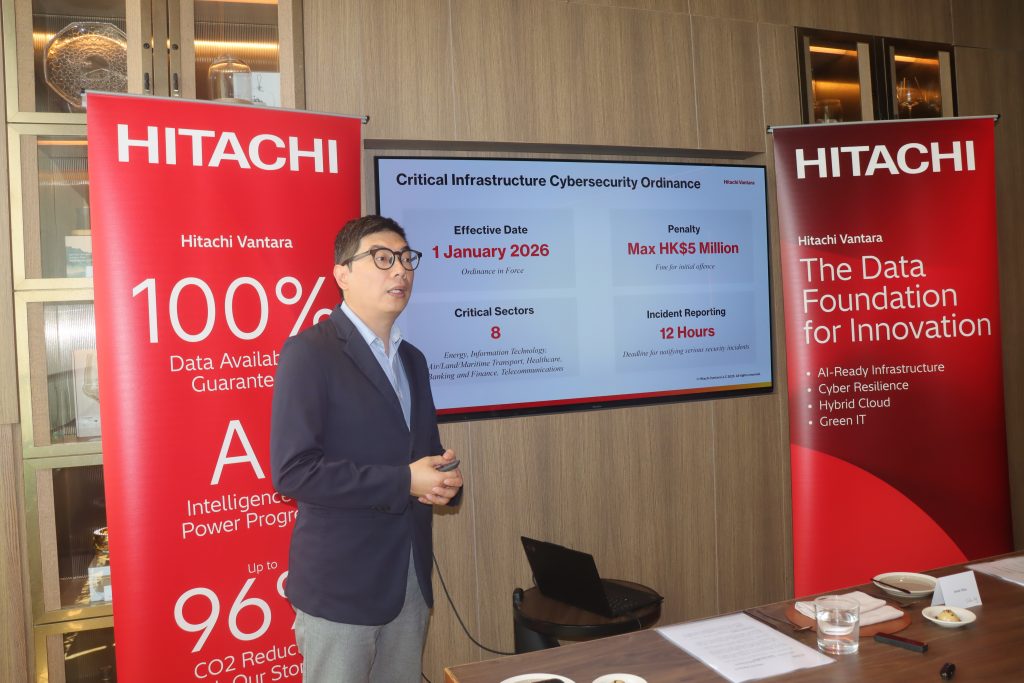
Douglas Lo, Director of Technical Sales for Hitachi Vantara Hong Kong & Taiwan, says the regulation will standardise how organisations operate critical infrastructure, but warns organisations must not be complacent. He offers four practical recommendations for operators:
Local control and accessibility
The regulation grants investigators the power to access data centres and directly inspect critical computer systems during security investigations. Operators that rely heavily on public cloud or overseas‑hosted infrastructure may find it difficult to meet these access requirements. Where possible, consider localised deployment or contractual arrangements that ensure investigators’ statutory access.
System availability and resilience
CIOs must develop and maintain business continuity and resilience plans to ensure core services remain operational even during cyber incidents. This includes redundancy, failover strategies, and regular testing under simulated attack scenarios.
Proactive vulnerability discovery and reporting
Regular security risk assessments are a core obligation under the regulation. Standard vulnerability scans may miss storage systems and other infrastructure components, so organisations should adopt more comprehensive assessment tools and processes, including supply‑chain and firmware vulnerability checks.
Rapid recovery to a clean state
Incident response and recovery plans must demonstrate that an organisation can restore critical services to a verified, clean state following a cybersecurity incident. This requires validated backup strategies, secure restoration procedures, and post‑incident forensics and validation.
Summary
The new regulation raises the bar for how critical infrastructure is protected. Organisations should treat it as both a compliance obligation and an operational imperative: accelerate investments in resilient, auditable data infrastructure; clarify cloud and hosting arrangements to meet access requirements; and strengthen detection, response, and recovery capabilities to reduce operational and public‑safety risks.

Leave a comment